Enterprise IaC Standardization
Manual VPC sprawl + quarterly audit pain → standardized IaC, 70% faster setup, findings down 47 → 3.
Reported engagement figures. See the results section for measurement context and limitations.
- Role
- Senior AWS Solution Architect
- Context
- Enterprise / Data & AI (NDA)
- Duration
- Ongoing (6+ months)
- Team
- 2 senior architects (me + 1) mentoring 8 junior engineers
Why they called
Fourteen VPCs had been built by hand across the accounts, with overlapping subnets, inconsistent CIDR ranges and no tagging. Every project carried its own security posture, a new environment took two to three weeks, drift was causing about a dozen incidents a month, and the quarterly security audit was returning 47 findings.
Tech stack
- AWS
- VPC
- RDS
- Terraform
- CloudFormation
- MySQL


Business problem and production context.
Business problem
Enterprise teams were provisioning AWS resources by hand, and every project had its own VPC layout, security posture and deployment pattern. That meant drift between environments, audit findings that came back every quarter, and new environments that took 2-3 weeks to stand up.
Architecture decision
With one other senior architect, I designed a reference architecture for VPC, compute and database, then encoded it as Terraform modules with secure defaults and documented overrides. Teams that do not write Terraform get the same patterns as Service Catalog products built on CloudFormation. Weekly review workshops with the junior engineers explained why each default exists, so the team can extend the modules without us.
Before and after.
Figures below come from the engagement account. Where no measurement source or period is provided, they are labelled reported. Workload scale, targets and engagement outcomes are different measures; past results are not a forecast for another system.
Teams provision AWS environments from reviewed modules with secure defaults instead of building them by hand, and every resource is checked for tags that drive cost reporting.
How a change becomes a provisioned environment and what checks it afterwards. The account structure, the workloads inside each environment and the module internals are not shown.
Main components only; supporting services are left out.
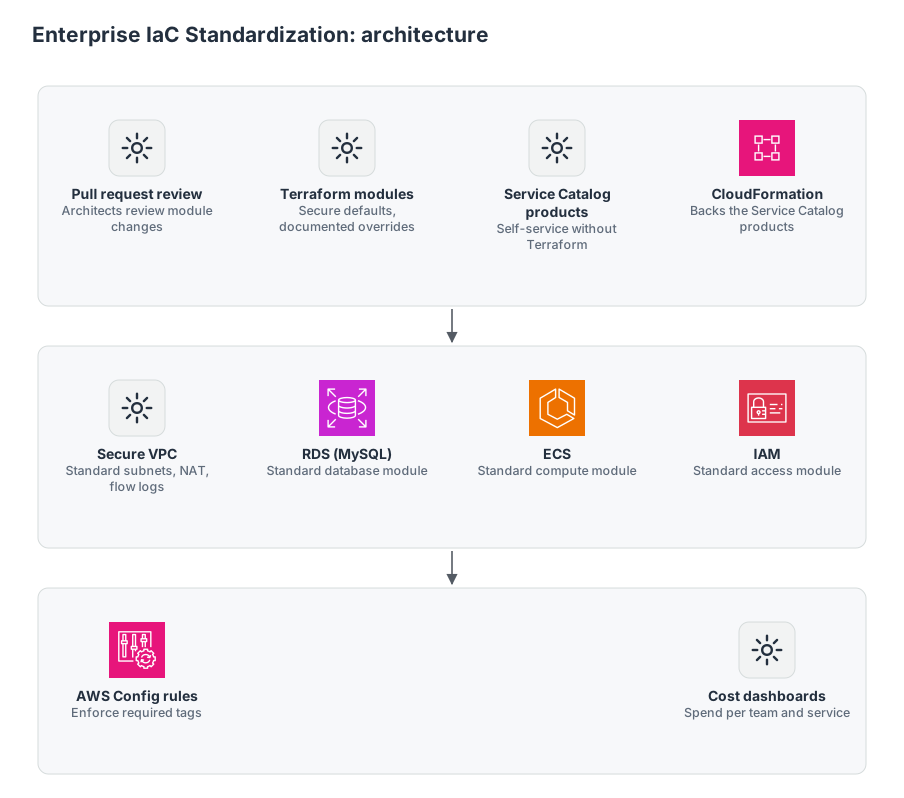
1. Provisioning paths
Pull request review
Architects review module changes
Terraform modules
Secure defaults, documented overrides
Service Catalog products
Self-service without Terraform

CloudFormation
Backs the Service Catalog products
2. Provisioned environment
Secure VPC
Standard subnets, NAT, flow logs

RDS (MySQL)
Standard database module

ECS
Standard compute module

IAM
Standard access module
3. Compliance and cost

AWS Config rules
Enforce required tags
Cost dashboards
Spend per team and service
How it works, step by step
- 1An engineer changes an environment through a pull request on the Terraform modules, reviewed with the architects in the weekly workshop.
- 2Terraform applies the VPC, RDS, ECS and IAM modules with their secure defaults, using a documented override only where a team needs one.
- 3Teams that do not write Terraform get the same patterns as Service Catalog products built on CloudFormation.
- 4AWS Config rules check the provisioned resources for the required tags.
- 5Those tags feed the per-team, per-service cost dashboards.
Guardrails
- Secure defaults in every module, with documented override escape hatches
- Consistent CIDR allocation with public, private and isolated subnets
- VPC flow logs on by default
- Pull request review of module changes
- Tagging enforced by AWS Config rules
Considered and not used
- AWS Landing Zone: Custom modules chosen for flexibility while keeping compliance guardrails.
- Aurora: RDS chosen for predictable workloads where Aurora's auto-scaling would add cost without benefit.
My part of the work, separate from the team's.
The team behind the engagement is in the facts row above. These are the parts I was responsible for, and the artifacts that show the work.
Owned scope
- Standardized cloud architecture templates with secure network, compute, and database patterns
- Reusable IaC patterns and workshops so junior engineers understood why decisions were made
- Enterprise guardrails around accounts, security, and repeatable provisioning
Evidence artifacts
What would fail first?
Every project has constraints. The useful work is naming them early enough that rollback, cost, and ownership are designed before an incident.
Enterprise compliance
Architecture needed to support secure defaults, repeatability, and audit-friendly implementation.
Team scaling
Junior engineers needed reusable patterns and decision context, not only templates.
Manual setup
Manual provisioning had to shrink so environments were consistent and easier to review.
Trade-offs accepted on purpose.
Production risks and how they were controlled.
Small steps, visible changes, fewer surprises.
- 01
Audited existing AWS accounts and found 14 manually provisioned VPCs with inconsistent CIDR ranges, overlapping subnets, and no tagging standards.
- 02
Designed a reference architecture with secure VPC templates: public/private/isolated subnets, NAT gateways, flow logs, and consistent CIDR allocation.
- 03
Built Terraform modules for VPC, RDS, ECS, and IAM with opinionated defaults. SOC2-compliant out of the box with override escape hatches.
- 04
Created AWS Service Catalog products using CloudFormation for teams that needed self-service provisioning without Terraform knowledge.
- 05
Led weekly architecture review workshops with junior engineers, reviewing their pull requests and explaining the trade-off behind each module default.
What the team runs now.
The point of the work is what the client's own engineers can change and operate without me.
- The Terraform modules for VPC, RDS, ECS and IAM, with SOC2 defaults and documented override escape hatches.
- Self-service provisioning through AWS Service Catalog for the teams that do not write Terraform.
- Tagging enforcement through AWS Config rules, and the per-team, per-service cost dashboards that depend on it.
- The architecture decisions themselves. Three of the junior engineers from the weekly review workshops now design compliant environments on their own.
What carries over to your system.
- Service Catalog was essential for adoption. Teams that weren't comfortable with Terraform could still self-service compliant infrastructure through a web UI.
- Tagging enforcement via AWS Config rules caught 90% of untagged resources within the first month. Without it, cost allocation would have remained invisible.
- Mentoring junior architects on WHY decisions were made (not just HOW) was the highest-leverage activity. Three of them now independently design compliant architectures.
Rollback path
Infrastructure templates needed versioned changes so teams could identify and revert risky updates.
Cost considerations
Cost control came from standard defaults, reviewable environment shape, and reducing accidental overbuild.
Observability notes
The baseline included account/environment visibility, template usage, security posture, and provisioning success.
Further reading
Services built on this work
Have a similar production problem?
Send the current architecture, bill concern, deployment pain, or GenAI reliability issue. I will help you find the first real bottleneck.
 Request the reliability audit